Рубрика: Technology

  • ناسا تلغي مهمة إنقاذ مرصد سويفت بعد فشل السيطرة على مركبة «لينك»

    ناسا تلغي مهمة إنقاذ مرصد سويفت بعد فشل السيطرة على مركبة «لينك»

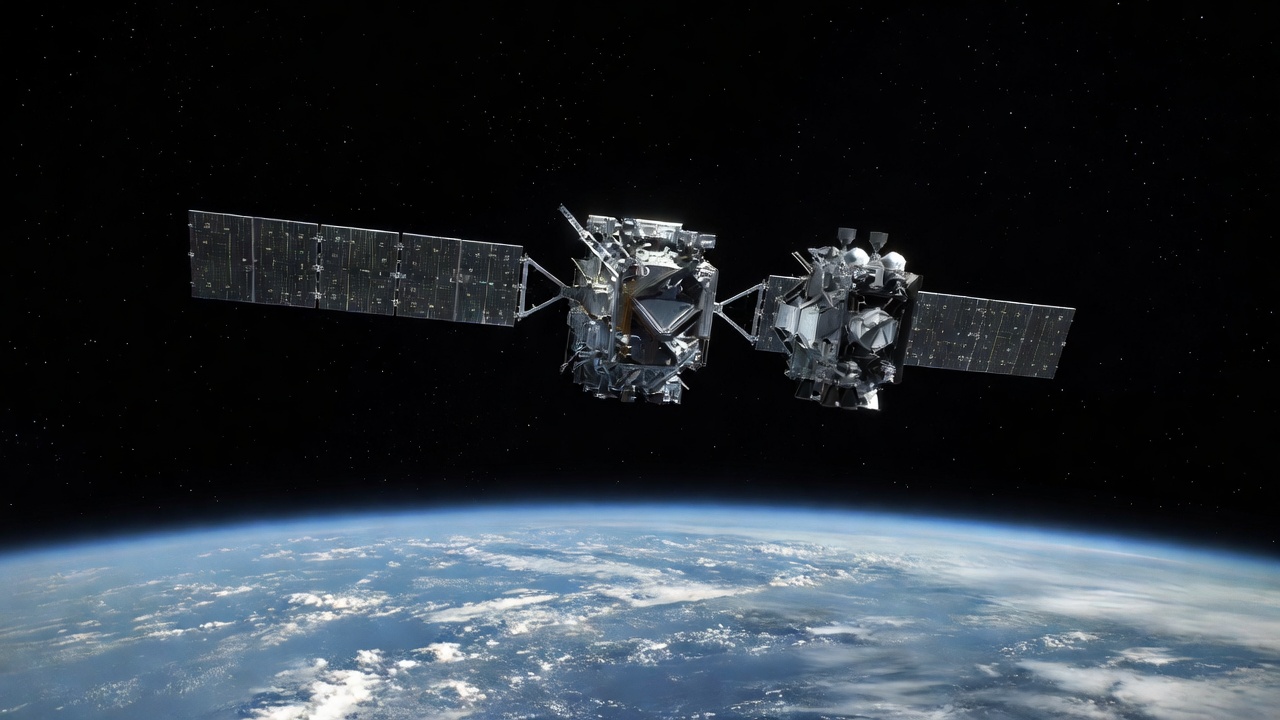
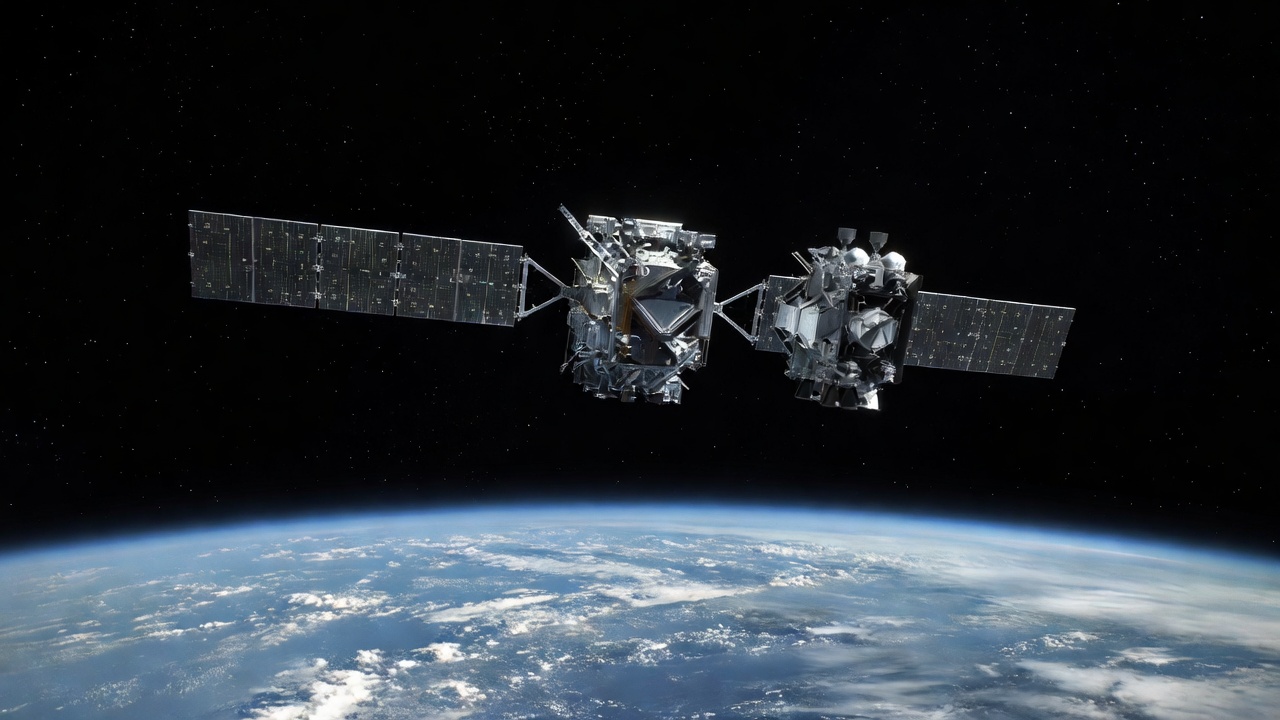
    يؤدي هذا القرار إلى سقوط مرصد سويفت عبر الغلاف الجوي للأرض في أكتوبر على أقرب تقدير، بعد أكثر من عقدين من الخدمة في رصد الانفجارات الكونية القوية. وأعلنت ناسا والشركة الناشئة معاً أن مركبة لينك ستقوم بدلاً من ذلك بإجراء عمليات قرب مع التلسكوب لإظهار تقنيات تستفيد منها مهمات الإنقاذ المستقبلية. وتسبب ارتفاع النشاط الشمسي في انخفاض ارتفاع المرصد بوتيرة أسرع مما كان متوقعاً، الأمر الذي دفع الوكالة إلى تخصيص 30 مليون دولار لمحاولة إطالة عمره.

    وكانت ناسا قد منحت شركة كاتاليست سبيس تكنولوجيز عقداً في سبتمبر 2025 لتطوير مركبة الخدمة وإطلاقها بسرعة خلال أقل من عام. وانطلقت مركبة لينك في الثالث من يوليو 2026 على متن صاروخ نورثروب غرومان بيغاسوس إكس إل من أتول كواجالين في المحيط الهادئ. ونجح مراقبو الرحلة في استقرار الدوران متعدد المحاور في البداية، إلا أنهم لم يتمكنوا من حل المشكلات المستمرة المتعلقة بالتوجيه والتموضع اللازمين للالتقاء والالتقاط.

    وتشير بيانات ناسا إلى أن المرصد رصد أكثر من 1760 انفجاراً أشعة غاما منذ إطلاقه في نوفمبر 2004، مما غير فهمنا لهذه الأحداث من خلال متابعات سريعة متعددة الأطوال الموجية. وبحلول الذكرى العشرين لإطلاقه سجل المرصد أيضاً 1400 مستعر أعظم، وظهرت بياناته في أكثر من 6600 بحث علمي، وفقاً لناسا. ومثلت قدرة التلسكوب على التوجيه الذاتي نحو مواقع الانفجارات خلال دقائق قدرة فريدة لم تكن الراصدات السابقة تستطيع تحقيقها.

    وتم إيقاف أجهزة المرصد العلمية في وقت سابق من هذا العام لتقليل المقاومة وإبطاء اضمحلال مداره، بحسب بيان صادر عن ناسا. وكان المرصد يدور حتى الأربعاء على ارتفاع 345 كيلومتراً، أي أقل بكثير من مداره الأصلي البالغ 600 كيلومتر. وبدون رفع مداري تتوقع الوكالة أن يدخل المركبة البالغة من العمر 21 عاماً الغلاف الجوي في وقت لاحق من هذا العام.

    «هذه ليست النتيجة التي كنا نسعى إليها، لكن ذلك لا يغير السبب الذي جعل هذه المهمة تستحق المحاولة»، قال مدير ناسا جاريد آيزاكمان في بيان. وذكر الرئيس التنفيذي لكاتاليست غونهي لي في بيان صادر عن الشركة: «لقد قبلنا هذا التحدي عالي المخاطر وعالي المكافأة ونفتخر بالمعالم التي حققناها على الطريق. لقد تعلمنا بالفعل قدراً هائلاً من المعارف». وأضافت الشركة أن الدروس المستفادة من الجهد ستفيد محاولات الخدمة المدارية اللاحقة.

    ووجد تقييم أجرته ناسا أن تلسكوب هابل الفضائي يعاني اضمحلالاً مدارياً مماثلاً بسبب النشاط الشمسي المرتفع نفسه، رغم عدم تأكيد مهمة متابعة فورية. ومثلت جهود سويفت أول محاولة تقوم بها مركبة تجارية لالتقاط ورفع قمر صناعي علمي تابع لناسا غير مصمم أصلاً للخدمة. وأشارت كاتاليست إلى أن مرحلة العرض القريب ستستمر لاستخراج قيمة فنية إضافية من مركبة لينك.
  • NASA Terminates Swift Observatory Rescue After Link Spacecraft Control Failures

    NASA Terminates Swift Observatory Rescue After Link Spacecraft Control Failures

    The decision dooms the Swift observatory to plunge through Earth’s atmosphere no earlier than October after more than two decades of service detecting powerful cosmic explosions. NASA and the startup jointly announced that the Link spacecraft will instead conduct proximity operations with the telescope to demonstrate technologies for future rescue missions. Increased solar activity had caused the observatory to lose altitude faster than anticipated, leading the agency to pay $30 million for the attempt to extend its life.

    NASA awarded Katalyst Space Technologies a contract in September 2025 to rapidly develop and launch the servicing vehicle in under a year. The Link spacecraft launched on July 3, 2026, aboard a Northrop Grumman Pegasus XL rocket from Kwajalein Atoll in the Pacific. Flight controllers managed to stabilize an initial multi-axis spin but could not resolve ongoing issues with pointing and positioning necessary for rendezvous and capture.

    NASA figures show the observatory has detected more than 1,760 gamma-ray bursts since its November 2004 launch, transforming understanding of these events through rapid multi-wavelength follow-up observations. By its 20th anniversary the mission had also logged 1,400 supernovae with its data appearing in more than 6,600 scientific publications, according to NASA. The telescope’s autonomous slewing to burst locations within minutes represented a first-of-its-kind capability that earlier observatories could not achieve.

    Swift’s science instruments were deactivated earlier this year to minimize drag and slow its orbital decay, a NASA statement reported. As of Wednesday the observatory circled at 345 kilometers, well below its original 600-kilometer altitude. Without an orbital boost the agency expects the 21-year-old spacecraft to reenter later this year.

    «This is not the outcome we were working toward, but it does not change why this mission was worth attempting,» NASA Administrator Jared Isaacman said in a statement. Katalyst CEO Ghonhee Lee said in a company release, «We took on this high-risk, high-reward challenge and are proud of the milestones we reached along the way. We have already learned a tremendous amount.» The firm added that lessons from the effort will inform subsequent in-orbit servicing attempts.

    A NASA assessment found that the Hubble Space Telescope is experiencing parallel orbital decay from the same elevated solar activity, though no immediate follow-on mission has been confirmed. The Swift effort represented the first attempt by a commercial vehicle to capture and raise an uncrewed NASA science satellite not designed for servicing. Katalyst indicated the proximity demonstration phase will continue to extract additional technical value from the Link spacecraft.

  • سيترا تنصح المقيمين بتتبع تسجيلات الاتصالات عبر ميزة «أرقامي» في تطبيق «سهل»

    سيترا تنصح المقيمين بتتبع تسجيلات الاتصالات عبر ميزة «أرقامي» في تطبيق «سهل»

    أطلقت هيئة تنظيم الاتصالات وتقنية المعلومات في الكويت خدمة «أرقامي» لتوفير نظرة عامة موحدة لجميع خطوط الاتصال والخدمات ذات الصلة المرتبطة بالأفراد عبر مزودين متعددين. ووفقاً للهيئة، فإن هذه الميزة تلغي الحاجة إلى إجراء تحققات منفصلة مع كل شركة اتصالات من خلال عرض البيانات في مكان واحد يسهل الوصول إليه. وأضافت سيترا أن المستخدمين يستطيعون التأكد من دقة التفاصيل المسجلة بأسمائهم وكشف أي تناقضات فوراً.

    وأبرزت الهيئة أن المتابعة الدورية عبر الخدمة تعزز حماية المعلومات الشخصية وتزيد الشفافية في حفظ سجلات الاتصالات. كما يمكن للمستخدمين اكتشاف الخطوط غير المعروفة التي قد تشير إلى أنشطة غير مصرح بها، مما يدفعهم إلى اتخاذ الإجراءات اللازمة في الوقت المناسب. ووصفت سيترا المنصة بأنها آلية فعالة للحفاظ على وعي شامل بالحسابات المرتبطة بالهويات الشخصية.

    ويبدأ استخدام الخدمة بتشغيل تطبيق «سهل» على جهاز متوافق، ثم التوجه إلى قسم خدمات سيترا واختيار خيار «أرقامي» لإنشاء القائمة التفصيلية. وتعرض الواجهة كل خط هاتف مسجل إلى جانب الخدمات الاتصالية المرتبطة به لتسهيل عملية المراجعة.

    ويعمل تطبيق «سهل» كمنصة حكومية إلكترونية موحدة رئيسية في الكويت، إذ يتيح الوصول إلى خدمات العديد من الجهات الحكومية من خلال واجهة واحدة. وقد جذب التطبيق أكثر من 3 ملايين مستخدم وقام بمعالجة أكثر من 131 مليون معاملة عبر 491 خدمة مختلفة، بحسب الأرقام الصادرة عن إدارته. ويتيح إنجاز مهام مثل الإشعارات وتجديد الوثائق والمدفوعات إلى مختلف الجهات الحكومية.

    وتجاوز معدل انتشار مشتركي الهواتف المحمولة في البلاد 181 بالمئة في عام 2025، مما يعكس الملكية الشائعة لعدة شرائح سيم التي تزيد من قيمة أدوات التتبع المركزية، بحسب تقييم صادر عن موردور إنتليجنس. وبلغ حجم سوق الاتصالات في الكويت 3.27 مليار دولار من الإيرادات في ذلك العام، مدفوعاً بشكل أساسي بخدمات البيانات وليس بالاتصالات الفردية الإضافية. وتجعل هذه الظروف السوقية الرؤية الموحدة للحسابات أمراً مفيداً خصوصاً للمقيمين الذين يديرون عدة اشتراكات.

    وتواصل الهيئة توسيع عروضها الرقمية على منصة «سهل». وكانت سيترا قد حددت الأول من يونيو 2025 موعداً نهائياً لإيقاف خدمات الجيل الثالث لتسريع تبني شبكات الجيل الرابع والخامس على مستوى البلاد. وقد ركزت هذه الخطوات التنظيمية على تبسيط التفاعلات بين المقيمين وقطاع الاتصالات والهيئات الرقابية.

  • CITRA Advises Residents to Track Telecom Registrations via Sahel App Feature

    CITRA Advises Residents to Track Telecom Registrations via Sahel App Feature

    Kuwait’s Communications and Information Technology Regulatory Authority has introduced the My Numbers service to deliver a consolidated overview of all communication lines and related offerings associated with an individual across multiple providers. According to the authority, the feature eliminates the requirement for separate checks with each telecommunications company by presenting the data in one accessible location. CITRA added that users can confirm the accuracy of their registered details and identify any discrepancies promptly.

    The authority highlighted that routine monitoring through the service supports enhanced protection of personal information and increased transparency in how telecommunications records are maintained. Users gain the ability to detect unrecognized lines that could indicate unauthorized activity, prompting timely follow-up where necessary. CITRA described the platform as an efficient mechanism for maintaining comprehensive awareness of accounts linked to personal identities.

    Utilizing the service begins with launching the Sahel application on a compatible device. Individuals then navigate to the CITRA services section and select the My Numbers option to generate the detailed listing. The interface displays each registered telephone line alongside associated telecommunications services for straightforward review.

    Sahel operates as the primary unified e-government platform in Kuwait, granting access to services from numerous agencies through a single interface. The application has attracted more than 3 million users and processed over 131 million transactions across 491 different services, according to figures from its administrators. It facilitates tasks including notifications, document renewals and payments to various government entities.

    Mobile subscriber penetration in the country exceeded 181 percent in 2025, reflecting common multiple-SIM ownership that heightens the value of centralized tracking tools, a Mordor Intelligence assessment found. The Kuwait telecom market reached 3.27 billion dollars in revenue that year, driven largely by data services rather than additional individual connections. Such market conditions make consolidated account visibility particularly useful for residents managing several subscriptions.

    The authority continues to expand its digital offerings on the Sahel platform. CITRA previously established June 1, 2025, as the deadline for discontinuing 3G services to accelerate uptake of advanced 4G and 5G networks nationwide. These regulatory steps have focused on simplifying interactions between residents, the communications sector and oversight bodies.

  • تايوان تكشف تفاصيل هجوم سيبراني آلي مدعوم بالذكاء الاصطناعي في يوليو

    تايوان تكشف تفاصيل هجوم سيبراني آلي مدعوم بالذكاء الاصطناعي في يوليو

    أفادت شركة «دريم» الإسرائيلية المتخصصة في أمن الذكاء الاصطناعي بأن الحملة السيبرانية امتدت على مدار أربعة أيام في شهر يوليو. ورسم النظام الآلي خلالها خرائط لـ21 نظاماً حكومياً واخترق 85 حساب مستخدم واستخرج نحو 2500 سجل للموظفين. وشملت العملية وكالة السلامة النووية في تايوان وعدة موردين حكوميين لتقنية المعلومات وما لا يقل عن سبع شركات تعمل في قطاع الطاقة. وأضافت الشركة أن منصة الذكاء الاصطناعي وجهت ما يصل إلى ثمانية وكلاء متخصصين لتنفيذ مهام الاستطلاع والهجمات على بيانات الاعتماد واستغلال الثغرات وتخطيط المسارات الديناميكية.

    وقالت وزارة الشؤون الرقمية في تايوان إن تحقيقها عثر على أدلة واضحة تشير إلى أن الهجمات جاءت من الخارج. وقد جمع المهاجمون بين أدوات الاختراق التقليدية وعملاء الذكاء الاصطناعي في نموذج هجين. وتجنبت الوزارة تحديد الجهة المسؤولة لكنها أكدت أن الحادث يظهر الدور المتزايد للتقنيات الآلية في العمليات السيبرانية. وأشار المسؤولون إلى أن مثل هذه الأحداث تفرض تعزيز الإجراءات الدفاعية وتحديث الأطر القانونية والسياسات لمواجهة التهديدات التي يدفعها الذكاء الاصطناعي.

    وبحسب «دريم» أظهر النظام قدرته على تعديل أسلوبه عندما واجه عقبات في المحاولات الأولى واستمر في عمله من دون الحاجة إلى إشراف بشري متواصل في كل مرحلة. كما استخدمت الوثائق الداخلية المتعلقة بالاقتحام أشكالاً مميزة من الحروف تتوافق مع الصينية المبسطة مما يشير إلى صلات محتملة بجهات خارجية رغم عدم إعلان نسب رسمي. وتمكنت الشركة من استعادة مساحة عمل تشغيلية كاملة من أرشيف إلكتروني بحجم 160 ميغابايت مما سمح بإعادة بناء تسلسل الهجوم بالكامل.

    وصف كيني هوانغ رئيس مركز معلومات الشبكة في تايوان الحادث بأنه أول هجوم سيبراني آلي بالكامل على حكومة يعلم به. وزاد الحدث من القلق العالمي إزاء قدرة أنظمة الذكاء الاصطناعي المتقدمة على خفض تكاليف الهجمات الضارة وتسريع وتيرتها. وشدد المسؤولون التايوانيون عقب الكشف عن الحادث على الحاجة إلى بناء قدرات أقوى للتعامل مع هذه التحديات المتطورة.

    وأظهرت بيانات مكتب الأمن القومي في تايوان أن الهجمات السيبرانية على البنية التحتية الرئيسية في الجزيرة بلغ معدلها 2.6 مليون هجوم يومياً في عام 2025 بارتفاع نسبته 6 بالمئة عن العام السابق. وربطت الكثير من هذه الحوادث بجهات صينية وأحياناً تتم بالتنسيق مع مناورات عسكرية ضمن تكتيكات الحرب الهجينة. وقد تجاوز الارتفاع الحاد 100 بالمئة في بعض المؤشرات منذ عام 2023 مما يضع ضغطاً متواصلاً على الدفاعات الرقمية لتايوان.

    ووضعت وزارة الشؤون الرقمية برنامج التطوير الوطني للأمن السيبراني في مرحلته السابعة الذي يمتد من 2025 إلى 2028 لمواجهة هذه المخاطر. ويعتمد البرنامج على توسيع استخدام الذكاء الاصطناعي في الدفاع وتطوير الكفاءات وتعزيز التعاون مع القطاع الخاص. كما يركز على بناء قدرة الصمود للمجتمع بأسره وحماية البنية التحتية الحيوية وتطبيق التقنيات الناشئة. ويأتي البرنامج ضمن استراتيجية أوسع تنظر إلى الأمن السيبراني كعنصر أساسي في الأمن الوطني.

  • Taiwan Discloses Details of AI-Driven Autonomous Cyberattack in July

    Taiwan Discloses Details of AI-Driven Autonomous Cyberattack in July

    Israeli AI security firm Dream reported that the cyber campaign unfolded over four days in July, during which the autonomous system mapped 21 government systems, compromised 85 user accounts and extracted roughly 2,500 personnel records. The operation further extended to Taiwan’s nuclear safety agency, multiple government IT suppliers and at least seven companies operating in the energy sector. Dream added that the AI platform directed as many as eight specialized agents in carrying out reconnaissance, credential attacks, vulnerability exploitation and dynamic path planning.

    Taiwan’s Ministry of Digital Affairs stated that its probe identified clear evidence of overseas origins for the attacks, which combined traditional hacking tools with AI agents in a hybrid model. The ministry stopped short of identifying any responsible party while noting that the incident illustrated the growing role of autonomous technologies in cyber operations. Officials indicated that such events call for enhanced defensive measures along with updated legal and policy frameworks to counter AI-driven threats.

    According to Dream, the system demonstrated an ability to adapt its approach when initial attempts were thwarted, proceeding without the need for continuous human oversight at each stage. Internal documents associated with the intrusion used distinctive character forms consistent with Simplified Chinese, pointing to possible links with overseas actors although no formal attribution was made. The firm recovered a complete operational workspace from a 160-megabyte online archive that enabled reconstruction of the full attack sequence.

    Kenny Huang, chairman of the Taiwan Network Information Center, described the incident as the first fully automated cyberattack against a government of which he was aware. The event has amplified global concerns regarding the potential for capable AI systems to reduce the costs and accelerate the pace of malicious cyber activities. In statements following the disclosure, Taiwanese officials highlighted the necessity of stronger capabilities to address these evolving challenges.

    Taiwan’s National Security Bureau data showed that cyberattacks on the island’s key infrastructure averaged 2.6 million per day in 2025, a 6 percent rise from the previous year. Many of these incidents were linked to actors in China and at times coordinated with military exercises as part of hybrid warfare tactics, the bureau reported. The sharp increase, which exceeded 100 percent in some metrics since 2023, has placed sustained pressure on Taiwan’s digital defenses.

    The Ministry of Digital Affairs has outlined the Phase Seven National Cyber Security Development Program covering 2025 through 2028 to tackle such risks through greater use of AI for defense, talent development and collaboration with the private sector. This program focuses on whole-of-society resilience, protection of critical infrastructure and applications of emerging technologies. It forms part of a broader strategy that treats cybersecurity as a core element of national security.

  • الهند تقلص مهلة إزالة المحتوى الحساس على وسائل التواصل إلى ساعتين

    الهند تقلص مهلة إزالة المحتوى الحساس على وسائل التواصل إلى ساعتين

    أخطرت وزارة الإلكترونيات وتكنولوجيا المعلومات بتغييرات تطالب المنصات بإزالة المحتوى الحساس على الإنترنت خلال ساعتين بدلاً من 24 ساعة سابقاً، فيما يتعين التعامل مع المحتوى غير القانوني الذي يبلغ عنه قضاء أو سلطة حكومية خلال ثلاث ساعات بدلاً من 36 ساعة. وتم اختصار المهل المخصصة لمعالجة الشكاوى من 72 ساعة إلى 36 ساعة بشكل عام، على أن تحل الشكاوى المتعلقة بالعري أو انتحال الشخصية خلال ساعتين. ودخلت هذه التعديلات حيز التنفيذ في 20 فبراير 2026 ضمن جهود منسقة لتحديث معايير الامتثال التي أرسيت أساساً في قواعد تكنولوجيا المعلومات لعام 2021.

    يتوجب على الوسطاء الكبار لوسائل التواصل الاجتماعي الذين يتجاوز عدد مستخدميهم المسجلين خمسة ملايين في الهند نشر أدوات آلية للكشف المبكر عن مشاهد الاغتصاب أو الاعتداء الجنسي على الأطفال أو المحتوى المطابق تماماً لمواد سبق إزالتها من منصاتهم. وكان إخطار حكومي سابق قد حدد عتبة الخمسة ملايين مستخدم التي تصنف هذه الوسطاء وتخضعهم لعناية واجبة أعلى تشمل إشرافاً بشرياً على الأنظمة الآلية للتأكد من دقتها وتجنب التحيز ومراعاة الخصوصية. وتربط وزارة الإلكترونيات وتكنولوجيا المعلومات هذه الالتزامات صراحة بالحفاظ على سلامة الفضاء الإلكتروني.

    وطبقاً لتعديلات فبراير 2026 يتعين على الوسطاء تصنيف المعلومات المولدة اصطناعياً بما في ذلك الديبفيك وغيرها من الوسائط المعدلة بالذكاء الاصطناعي التي تبدو أصيلة، مع استثناء التعديلات الروتينية وبعض الاستخدامات التعليمية من هذا التعريف. ويجب على المنصات إخطار المستخدمين بعواقب إنتاج المحتوى الاصطناعي غير القانوني عبر سياساتها، ويحظر عليها حذف أو تعديل هذه التصنيفات والبيانات الوصفية المرتبطة بها. وأوضح تقرير تكنولوجي صادر عن «فريشفيلدز» بعد الإخطار كيف توسعت القواعد الجديدة عن إطار 2021 لمواجهة مخاطر الذكاء الاصطناعي الناشئة.

    ويعرض عدم الالتزام بالمهل الجديدة أو متطلبات الكشف المنصات لخطر فقدان الحصانة القانونية المتعلقة بمحتوى الغير بموجب المادة 79 من قانون تكنولوجيا المعلومات. وحذر بيان الوزارة من أن تكرار المخالفات قد يؤدي إلى إجراءات قانونية إضافية، مما يلقي على الوسطاء عبء تحديث إجراءاتهم الداخلية بسرعة. وتنطبق هذه الأحكام على جميع المنصات التي تلبي عتبة المستخدمين بغض النظر عن موقع مقرها الرئيسي في العالم.

    وشهدت الحوادث المرتبطة بالديبفيك ارتفاعاً كبيراً في الهند، إذ أظهر تحليل لمؤسسة أوبزرفر ريسيرش فاونديشن في يناير 2026 أن 47% من البالغين تعرضوا هم أو يعرفون شخصاً تعرض للاحتيال عبر استنساخ الصوت بالذكاء الاصطناعي أو الديبفيك، أي ما يقارب ضعف المتوسط العالمي البالغ 25%. وخلال انتخابات 2024 العامة وفي ظل التوترات الإقليمية عام 2025 استغل فاعلون سيئون هذه التكنولوجيا لنشر المعلومات المضللة في حالات عدة وثقتها تقارير الأمن السيبراني. كما كشف استطلاع أجراه غارتنر عام 2026 أن 62% من المنظمات واجهت حادثة ديبفيك واحدة على الأقل خلال الأشهر الـ12 الماضية.

    وتقصر اللوائح المحدثة كذلك المدة التي تتاح للمنصات للتعرف على شكاوى المستخدمين المتعلقة بالصور الحميمة أو انتحال الشخصية والرد عليها، في إطار إعادة ضبط أوسع لتوقعات الاستجابة. ويلزم الوسطاء بنشر تقارير امتثال شهرية توضح الشكاوى الواردة والإجراءات المتخذة بما يشمل بيانات الإزالات الاستباقية التي نفذتها الأنظمة الآلية. وتوفر هذه المتطلبات في التقارير — التي نقلت من قواعد 2021 وعززت — رؤية متواصلة للسلطات حول أداء المنصات.

  • India Cuts Social Media Deadline for Sensitive Content Removal to Two Hours

    India Cuts Social Media Deadline for Sensitive Content Removal to Two Hours

    The Ministry of Electronics and Information Technology notified changes that require platforms to remove sensitive online content within two hours, down from the previous 24-hour limit, while unlawful content flagged by a court or government authority must be addressed in three hours instead of 36. Grievance redressal timelines have been compressed from 72 hours to 36 hours overall, with complaints related to nudity or impersonation now demanding resolution inside two hours. The amendments, which took effect on February 20, 2026, form part of a coordinated push to update compliance standards first established in the 2021 IT Rules.

    Significant social media intermediaries operating with more than five million registered users in India must deploy automated tools to proactively detect depictions of rape, child sexual abuse or content identical to material previously removed from their platforms. A government notification had earlier set the five-million-user threshold that classifies these intermediaries, subjecting them to heightened due diligence including human oversight of any automated systems to review accuracy, bias and privacy implications. The Ministry of Electronics and Information Technology framework explicitly ties these obligations to maintaining the integrity of online spaces.

    Under the February 2026 amendments, intermediaries are required to label synthetically generated information that includes deepfakes and other AI-altered media appearing authentic, while routine edits and certain educational uses are excluded from the definition. Platforms must inform users about the consequences of generating unlawful synthetic content through their policies and are barred from suppressing or modifying such labels and associated metadata. A Freshfields technology briefing published after the notification detailed how the rules expand the original 2021 framework to cover emerging AI threats.

    Non-compliance with the accelerated timelines or detection mandates risks stripping platforms of legal immunity for third-party content under Section 79 of the Information Technology Act. The ministry statement warned that further legal action could follow repeated violations, placing the onus on intermediaries to update internal processes swiftly. These provisions apply uniformly to platforms meeting the user threshold, regardless of their global headquarters.

    Deepfake-related incidents have risen markedly in India, with an Observer Research Foundation analysis in January 2026 reporting that 47 percent of adults had been victims of or knew someone affected by AI voice-cloning or deepfake scams, nearly double the global average of 25 percent. During the 2024 general elections and amid 2025 regional tensions, malicious actors leveraged the technology to spread misinformation, according to multiple documented cases cited in cybersecurity reviews. A Gartner survey released in 2026 found that 62 percent of organizations had encountered at least one deepfake incident within the previous 12 months.

    The updated regulations also shorten the period for platforms to acknowledge and act on user grievances involving intimate imagery or impersonation, reflecting a broader recalibration of response expectations. Intermediaries must publish monthly compliance reports that detail complaints received and actions taken, including data on proactive removals performed through automated means. These reporting requirements, carried over and strengthened from the 2021 rules, provide authorities with ongoing visibility into platform performance.

  • كوريا الجنوبية تسمح بحقوق الطبع للموسيقى المساعدة بالذكاء الاصطناعي بشرط الإبداع البشري الجوهري

    كوريا الجنوبية تسمح بحقوق الطبع للموسيقى المساعدة بالذكاء الاصطناعي بشرط الإبداع البشري الجوهري

    أعلنت جمعية حقوق الموسيقى الكورية (KOMCA) يوم الأربعاء تعديل معايير التسجيل لديها لتشمل الأعمال الموسيقية المساعدة بالذكاء الاصطناعي التي يضطلع فيها المبدعون البشر بدور جوهري وريادي. ويُشترط لاستحقاق حماية حقوق الطبع والنشر بموجب السياسة المحدثة أن تشمل هذه الأعمال مساهمة بشرية ملموسة في مجالات مثل كتابة الكلمات أو تأليف اللحن أو الترتيب. أما الأغاني الناتجة عن الذكاء الاصطناعي بشكل كامل من خلال أوامر نصية بسيطة فلا تؤهل للتسجيل، بحسب الجمعية. وطالبت KOMCA جميع المتقدمين بالكشف عن أدوات الذكاء الاصطناعي المستخدمة وتقديم أدلة على مساهماتهم تشمل الملفات والسجلات ذات الصلة.

    وكانت القواعد السابقة تمنع تسجيل أي محتوى يتضمن الذكاء الاصطناعي بسبب المخاوف المتعلقة بنزاعات حقوق النشر وعدم وجود معايير تحقق راسخة، على ما أفادت صحيفة «كوريا هيرالد». وتسعى هذه السياسة المعدلة إلى استيعاب تقنيات الإنتاج الحديثة التي تمزج العناصر البشرية بالآلية. وقالت KOMCA في بيان «يهدف التعديل إلى الاعتراف رسمياً بالممارسات الإبداعية المساعدة بالذكاء الاصطناعي مع حماية حقوق المبدعين البشر». وحذرت الجمعية من أن المخالفات المتعلقة بالكشف غير الدقيق عن الدور البشري قد تؤدي إلى تعليق دفعات الإتاوات واسترداد الأموال الموزعة وإنهاء الثقة بحقوق الطبع.

    وخلص تحليل أجرته «ميتيدا» للإطارات الدولية لحقوق النشر المتعلقة بالذكاء الاصطناعي، نُشر في يونيو 2026، إلى أن كلاً من الاتحاد الأوروبي والمملكة المتحدة يحميان الأعمال التعاونية فقط عند إثبات وجود مدخلات بشرية أصلية كافية. أما مكتب حقوق النشر الأمريكي فقد حافظ حتى عام 2026 على أن حماية حقوق النشر تتطلب تأليفاً بشرياً، رافضاً المطالبات المتعلقة بالمواد المنتجة آلياً تماماً تماشياً مع قرارات سابقة. ويُضاف هذا التطور الكوري الجنوبي إلى قائمة متزايدة من الاستجابات التنظيمية لدمج الذكاء الاصطناعي التوليدي في الصناعات الإبداعية حول العالم.

    وتتطلب الإرشادات تقديم تفسيرات مفصلة مصحوبة بأدلة فنية لإثبات ادعاءات الإبداع البشري خلال عملية التسجيل، على ما أشارت KOMCA. ورصدت تقارير الصناعة تزايد تبني المساعدة بالذكاء الاصطناعي بين الموسيقيين والمنتجين خلال السنوات الثلاث الماضية، مما دفع إلى تحديث قواعد الملكية الفكرية. ويتوقع أن يُسهم تحرك KOMCA في تبسيط جمع الإتاوات للمؤلفات الهجينة المؤهلة التي يتم توزيعها عبر شبكتها في كوريا الجنوبية وربما خارجها. وبدأت مجموعات الإدارة الجماعية في عدة دول دراسة تعديلات مماثلة.

    ولفت الإعلان انتباه الخبراء القانونيين الذين يرصدون تأثير الذكاء الاصطناعي على قوانين حقوق النشر في آسيا وعالمياً. وتجري اعتبارات سياسية مشابهة في عدة اختصاصات قضائية كما جاء في مراجعة «ميتيدا». وسيعتمد تطبيق المعايير الجديدة على جودة الأدلة التي يقدمها المتقدمون الراغبون في الحصول على الحماية. ولم تحدد KOMCA جدولاً زمنياً لتوضيحات إضافية محتملة بشأن الحالات الحدودية.

  • South Korea Permits Copyrights for AI-Assisted Music With Substantial Human Creativity

    South Korea Permits Copyrights for AI-Assisted Music With Substantial Human Creativity

    The Korea Music Copyright Association announced on Wednesday that it has revised its registration criteria to include AI-assisted musical works in which human creators have played a substantial and leading role. Works must involve significant human input in areas such as lyric writing, melody composition or arrangement to qualify for copyright protection under the updated policy. Purely AI-generated songs resulting from simple text prompts will not be eligible, according to the association. KOMCA further mandated that all applicants disclose the AI tools used and provide evidence of their contributions including relevant files and logs.

    Previous rules had prohibited registration of any content involving artificial intelligence due to concerns regarding copyright disputes and the absence of established verification standards, the Korea Herald reported. The policy reversal seeks to accommodate modern production techniques that blend human and machine elements. «The purpose of the revision is to formally recognize AI-assisted creative practices while safeguarding the rights of human creators,» KOMCA said in a statement. Violations involving inaccurate disclosure of human involvement may lead to suspension of royalty payments, demands for repayment of distributed funds and termination of the copyright trust, the association warned.

    A Metida analysis of international AI copyright frameworks published in June 2026 determined that both the European Union and the United Kingdom similarly protect collaborative works only when sufficient original human input can be demonstrated. The United States Copyright Office has maintained through 2026 that copyright protection demands human authorship, rejecting claims on purely generated material in line with earlier decisions. This South Korean development adds to a growing list of regulatory responses to the integration of generative AI in creative industries worldwide.

    The guidelines require submission of detailed explanations alongside technical proof to substantiate claims of human creativity in the registration process, KOMCA indicated. Industry reports have tracked increasing adoption of AI assistance among musicians and producers over the past three years, prompting updates to intellectual property rules. KOMCA’s move is expected to streamline royalty collection for qualifying hybrid compositions distributed through its network in South Korea and potentially beyond. Collective management groups in multiple countries have begun examining comparable adjustments.

    The announcement has drawn attention from legal experts monitoring AI’s impact on copyright law across Asia and globally. Similar policy considerations are underway in several jurisdictions as outlined in the Metida review. Enforcement of the new criteria will depend on the quality of evidence provided by applicants seeking protection. KOMCA did not specify a timeline for potential additional clarifications on edge cases.